
diff options
| -rw-r--r-- | .github/workflows/build-iso.yml | 103 | ||||
| -rw-r--r-- | README.md | 22 | ||||
| -rw-r--r-- | iso.toml | 2 |
3 files changed, 123 insertions, 4 deletions
diff --git a/.github/workflows/build-iso.yml b/.github/workflows/build-iso.yml new file mode 100644 index 0000000..1083249 --- /dev/null +++ b/.github/workflows/build-iso.yml @@ -0,0 +1,103 @@ +--- +name: Build ISOs + +on: + workflow_dispatch: + inputs: + upload-to-s3: + description: "Upload to S3" + required: false + default: false + type: boolean + platform: + required: true + type: choice + options: + - amd64 + - arm64 + pull_request: + branches: + - main + paths: + - './iso.toml' + - './.github/workflows/build-iso.yml' + - './Justfile' + +env: + IMAGE_REGISTRY: "ghcr.io/${{ github.repository }}" + DEFAULT_TAG: "latest" + +concurrency: + group: ${{ github.workflow }}-${{ github.ref || github.run_id }} + cancel-in-progress: true + +jobs: + build: + name: Build ISOs + runs-on: ${{ inputs.platform == 'amd64' && 'ubuntu-24.04' || 'ubuntu-24.04-arm' }} + strategy: + fail-fast: false + permissions: + contents: read + packages: read + id-token: write + + steps: + - name: lower case the image registry in case of any capitalization + run: | + echo "IMAGE_REGISTRY=${IMAGE_REGISTRY,,}" >> ${GITHUB_ENV} + + - name: Install dependencies + if: inputs.platform == 'arm64' + run: | + set -x + sudo apt update -y + sudo apt install -y \ + podman + + - name: Maximize build space + if: inputs.platform != 'arm64' + uses: ublue-os/remove-unwanted-software@cc0becac701cf642c8f0a6613bbdaf5dc36b259e # v9 + with: + remove-codeql: true + + - name: Checkout + uses: actions/checkout@11bd71901bbe5b1630ceea73d27597364c9af683 # v4 + + - name: Setup Just + uses: extractions/setup-just@dd310ad5a97d8e7b41793f8ef055398d51ad4de6 # v2 + + - name: Build ISO + id: build + uses: ublue-os/bootc-image-builder-action@main + with: + bootc-image-builder-image: ghcr.io/centos-workstation/bootc-image-builder:latest + use-librepo: true + config-file: ./iso.toml + image: ${{ env.IMAGE_REGISTRY }}:${{ env.DEFAULT_TAG }} + + - name: Upload ISOs and Checksum to Job Artifacts + if: inputs.upload-to-s3 != true && github.event_name != 'pull_request' + uses: actions/upload-artifact@4cec3d8aa04e39d1a68397de0c4cd6fb9dce8ec1 # v4 + with: + path: ${{ steps.build.outputs.output-directory }} + if-no-files-found: error + retention-days: 0 + compression-level: 0 + overwrite: true + + - name: Upload to S3 + if: inputs.upload-to-s3 == true && github.event_name != 'pull_request' + shell: bash + env: + RCLONE_CONFIG_S3_TYPE: s3 + RCLONE_CONFIG_S3_PROVIDER: ${{ secrets.S3_PROVIDER }} + RCLONE_CONFIG_S3_ACCESS_KEY_ID: ${{ secrets.S3_ACCESS_KEY_ID }} + RCLONE_CONFIG_S3_SECRET_ACCESS_KEY: ${{ secrets.S3_SECRET_ACCESS_KEY }} + RCLONE_CONFIG_S3_REGION: ${{ secrets.S3_REGION }} + RCLONE_CONFIG_S3_ENDPOINT: ${{ secrets.S3_ENDPOINT }} + SOURCE_DIR: ${{ steps.build.outputs.output-directory }} + run: | + sudo apt-get update + sudo apt-get install -y rclone + rclone copy $SOURCE_DIR S3:${{ secrets.S3_BUCKET_NAME }}
\ No newline at end of file @@ -47,9 +47,9 @@ This file defines the operations used to customize the selected image. It contai ## Building an ISO -Modify `iso.toml` to point to your custom image before generating an ISO. +This template provides an out of the box workflow for getting an ISO image for your custom OCI image which can be used to directly install onto your machines. -- (Steps in progress) +This template provides a way to upload the ISO that is generated from the workflow to a S3 bucket or it will be available as an artifact from the job. To upload to S3 we use a tool called [rclone](https://rclone.org/) which is able to use [many S3 providers](https://rclone.org/s3/). For more details on how to configure this see the details [below](#build-isoyml). ## Workflows @@ -57,6 +57,22 @@ Modify `iso.toml` to point to your custom image before generating an ISO. This workflow creates your custom OCI image and publishes it to the Github Container Registry (GHCR). By default, the image name will match the Github repository name. +### build-iso.yml + +This workflow creates an ISO from your OCI image by utilizing the [bootc-image-builder](https://osbuild.org/docs/bootc/) to generate an ISO. In order to use this workflow you must complete the following steps: + +- Modify `iso.toml` to point to your custom image before generating an ISO. +- If you changed your image name from the default in `build.yml` then in the `build-iso.yml` file edit the `IMAGE_REGISTRY` and `DEFAULT_TAG` environment variables with the correct values. If you did not make changes, skip this step. +- Finally, if you want to upload your ISOs to S3 then you will need to add your S3 configuration to the repository's Action secrets. This can be found by going to your repository settings, under `Secrets and Variables` -> `Actions`. You will need to add the following + - `S3_PROVIDER` - Must match one of the values from the [supported list](https://rclone.org/s3/) + - `S3_BUCKET_NAME` - Your unique bucket name + - `S3_ACCESS_KEY_ID` - It is recommended that you make a separate key just for this workflow + - `S3_SECRET_ACCESS_KEY` - See above. + - `S3_REGION` - The region your bucket lives in. If you do not know then set this value to `auto`. + - `S3_ENDPOINT` - This value will be specific to the bucket as well. + +Once the workflow is done, you'll find it either in your S3 bucket or as part of the summary under `Artifacts` after the workflow is completed. + #### Container Signing Container signing is important for end-user security and is enabled on all Universal Blue images. It is recommended you set this up, and by default the image builds *will fail* if you don't. @@ -79,7 +95,7 @@ This provides users a method of verifying the image. 3. Add the private key to GitHub - - This can also be done manually. Go to your repository settings, under Secrets and Variables -> Actions + - This can also be done manually. Go to your repository settings, under `Secrets and Variables` -> `Actions` 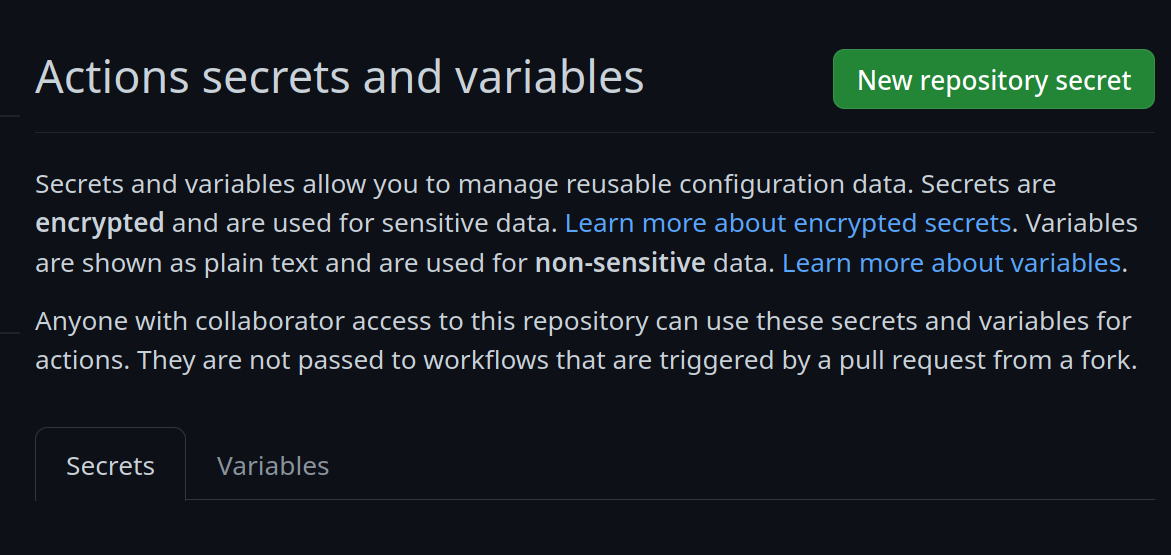 Add a new secret and name it `SIGNING_SECRET`, then paste the contents of `cosign.key` into the secret and save it. Make sure it's the .key file and not the .pub file. Once done, it should look like this: 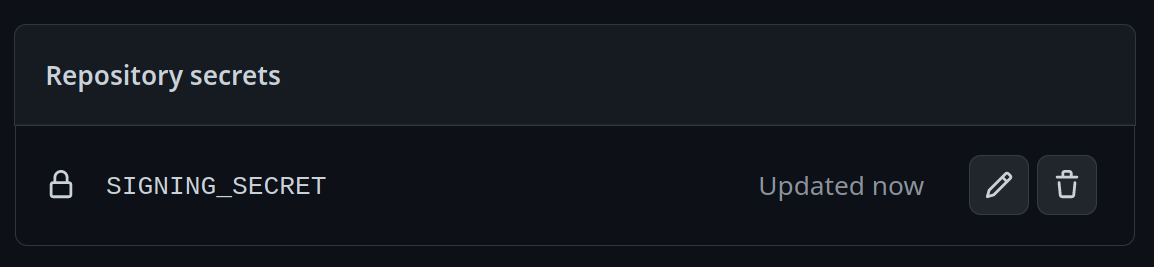 @@ -1,7 +1,7 @@ [customizations.installer.kickstart] contents = """ %post -bootc switch --mutate-in-place --transport registry ghcr.io/yourname/yourusername:latest +bootc switch --mutate-in-place --transport registry ghcr.io/yourrepo/yourimage:latest %end """ |